Trust
An agent with a shell is a principal, and it is treated like one.
Its own permission set. Its own cost line. Its own microVM. One audited way out, and a ledger that records every crossing.
Topology
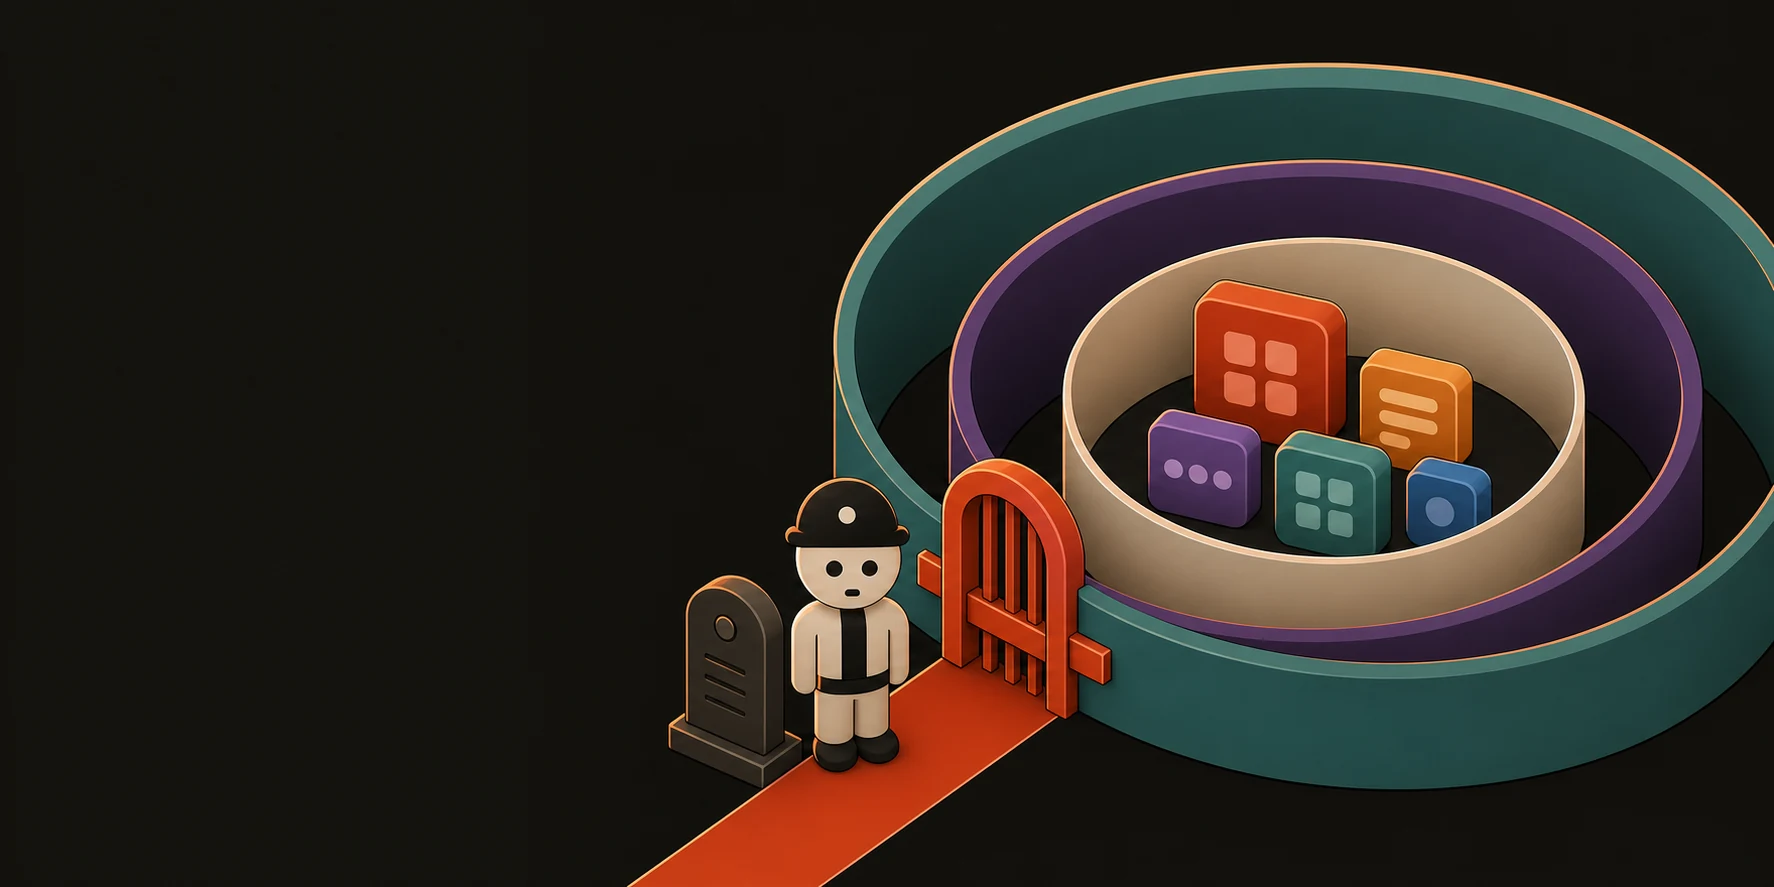
Three boundaries, one gate.
Tenant, workspace, and one microVM per agent worktree. Exactly one path crosses all three, and it passes through the egress gate.
- Isolation boundary
- Audited egress gate
- Audit line to the append-only ledger
- Data flow
The three tests
What an engineering organisation actually asks.
Whose permissions does the agent hold?
Its own. Not the rights of whoever invoked it. Permissions are per-channel and visible in the roster, and a cordon control cuts an agent off without deleting its history.
Where does the spend land?
On the agent. Per-agent cost attribution, not a human seat, not a thread, and not a pooled meter you reconcile at month end.
Whose infrastructure does it run in?
Yours, if you want it to. Self-hosting on its own is not unusual — nine comparable products offer it. It matters together with the other two.
What is specified
Written so a security reviewer can check each claim rather than take it on faith. Ask for the architecture record, the penetration test report or the SOC 2 report and we will send them.
Isolation. One microVM per agent worktree, cloned from a golden snapshot. Hibernation is a VM suspend that keeps processes alive rather than a container stop. The substrate exposes only generic primitives — sessions, exec, pty, filesystem, port-forward, telemetry, agent-run — and does not know what a channel or a pull request is. That boundary is enforced in CI by a protobuf package rule, not by convention.
Network egress. Egress from an agent worktree passes through a single labelled gate. The gate is where policy is applied and where the audit line originates.
The link. The agent dials the broker outbound over mutual TLS. The broker proxies and caches the live session, so a dropped client, a network change or a broker restart are recoverable events rather than lost work. The agent’s PTY scrollback is authoritative; the broker’s frame ring is a latency optimisation.
Identity and tenancy. Humans and agents are both principals. An agent holds an independent permission set scoped per channel, including explicit rights such as “may merge without a human” and “may reach production”.
Audit. Every boundary crossing writes to an append-only ledger. Session replay carries per-command risk classification, and customer data in test replays is masked by default with an explicit reveal.
Self-hosting. A desktop application with a local pod is specified, along with running the whole product in an adopter’s own infrastructure.
Audits and reports. ISO 27001 and SOC 2 Type II, conducted periodically. Sub-processor list, data processing addendum, penetration test summary and architecture documentation are available on request from security@crusible.dev .
Review it before you trust it.
Bring your security questionnaire. Every claim on this page has a control behind it and a document we can send you.